Lab practice’s creating VPC, subnets, an Internet Gateway, a route table and configuring these services to work together.
Lab 91
Services Covered
 Amazon EC2
 Elastic IP address
 AWS CLI
 Internet Gateway
Lab description
Lab practice’s creating VPC, subnets, an Internet Gateway, a route table and configuring these services to work together. Then EC2 instance will be launched into the VPC and a page hosted on that instance using AWS CLI commands. Lab includes:
- Usage of AWS CLI
- Creating EC2 Instances
- Creating VPCs, Internet Gateway, Route Table
- Allocating and assigning Elastic IP address to the EC2 Instance
- Creating subnets and Security Group Rules
Lab date
01-10-2021
Prerequisites
- AWS account
- putty for SSH connection
Lab steps
- In IAM create role for EC2 instance attach the AmazonEC2FullAccess permission to it.
- In EC2 launch an Amazon Linux 2 instance of type t2.micro. Then attach the created IAM role to it. Configure and assign a new security group that will allow SSH connections into the instance. Create and download new key pair.
- Connect to the instance using SSH and provided key pair.
- Create a VPC using AWS CLI. Run this command and change region accordingly:
aws ec2 create-vpc --cidr-block 10.1.0.0/16 --region us-east-1 Copy and save the VPC ID

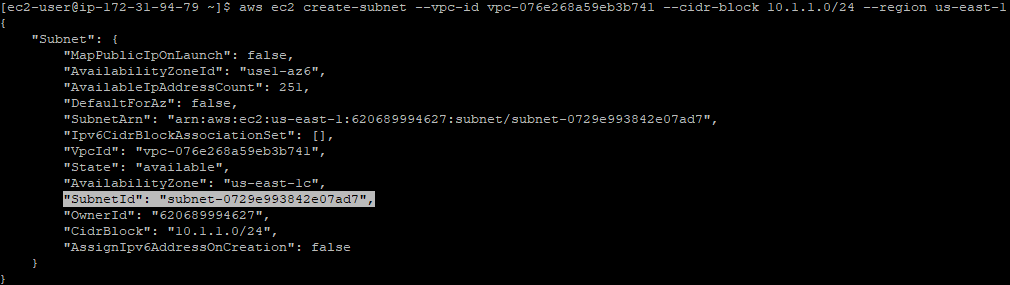
- Create a Subnet within the VPC
aws ec2 create-subnet --vpc-id vpc-076e268a59eb3b741 --cidr-block 10.1.1.0/24 --region us-east-1Replace the VPC with yours. Note the SubnetID
- Create an Internet Gateway
aws ec2 create-internet-gateway --region us-east-1
- Attach Internet Gateway to VPC. Replace VPC and IG ids with yours
aws ec2 attach-internet-gateway --vpc-id vpc-076e268a59eb3b741 --internet-gateway-id igw-062ea96ac99246cb4 --region us-east-1 - Create a Route table for VPC. Note the RouteTableID
aws ec2 create-route-table --vpc-id vpc-076e268a59eb3b741 --region us-east-1
- Create a public route in the Route table pointing to the Internet Gateway. Replace Route Table and Gateway ids with yours.
aws ec2 create-route --route-table-id rtb-0f79711b81e6401b5 --destination-cidr-block 0.0.0.0/0 --gateway-id igw-062ea96ac99246cb4 --region us-east-1 - Associate the Subnet with your Route table
aws ec2 associate-route-table --subnet-id subnet-0729e993842e07ad7 --route-table-id rtb-0f79711b81e6401b5 --region us-east-1 - Create a Security Group
aws ec2 create-security-group --group-name my-sg --description "My security group" --region us-east-1 --vpc-id vpc-076e268a59eb3b741Note the security group ID.
- Add Rules allowing traffic for HTTP on port 80 and SSH on port 22
aws ec2 authorize-security-group-ingress --group-id sg-0770cff403a4005c7 --protocol tcp --port 80 --cidr 0.0.0.0/0 --region us-east-1aws ec2 authorize-security-group-ingress --group-id sg-0770cff403a4005c7 --protocol tcp --port 22 --cidr 0.0.0.0/0 --region us-east-1 - Create a KeyPair
aws ec2 create-key-pair --key-name MyCLIKeyPair --query 'KeyMaterial' --region us-east-1 - Create user data file.
nano data.txtWith following contents that will install a php server called httpd with an index html site and start the service:
#!/bin/bash
sudo su
yum update -y
yum install httpd -y
echo "<html><h1>Welcome to Whizlabs Server</h1><html>" >> /var/www/html/index.html
systemctl start httpd
systemctl enable httpd
Save the file.
- Create another t2.micro EC2 Instance with Amazon Linux 2 with the user data:
aws ec2 run-instances --image-id ami-062f7200baf2fa504 --count 1 --instance-type t2.micro --key-name MyCLIKeyPair --region us-east-1 --security-group-id sg-0770cff403a4005c7 --user-data file://./data.txt --subnet-id subnet-0729e993842e07ad7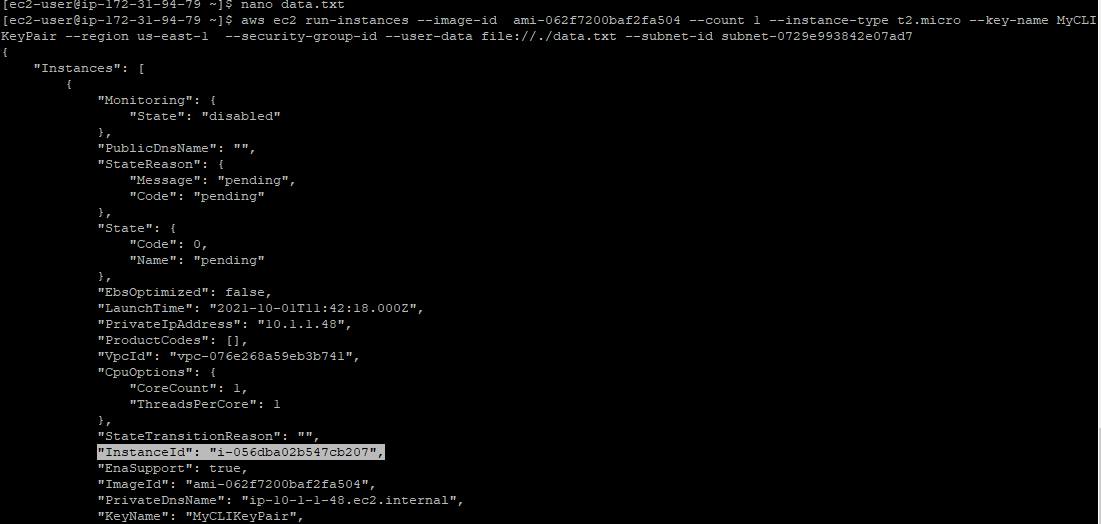
Note the new EC2 ID.
- Allocate an Elastic Ip address and note the AllocationID from the output
aws ec2 allocate-address --domain vpc --region us-east-1
- Associate the Elastic IP Address with the EC2 Instance (with your IDs)
aws ec2 associate-address --instance-id i-0b1f210708cc97bbf --allocation-id eipalloc-06387267b6f8733c2 --region us-east-1Go to the PublicIp address and check if everything works.
- Don’t forget to stop the instances:
aws ec2 stop-instances --instance-ids i-056dba02b547cb207 --region us-east-1Disassociate Elastic IP address:
aws ec2 disassociate-address --association-id eipassoc-0bcac2ed3d4837f86 --region us-east-1Release an Elastic IP address:
aws ec2 release-address --allocation-id eipalloc-06387267b6f8733c2 --region us-east-1Delete subnet, Internet Gateway and Route Table:
aws ec2 delete-internet-gateway --internet-gateway-id igw-062ea96ac99246cb4 --region us-east-1aws ec2 delete-route-table --route-table-id rtb-0f79711b81e6401b5 --region us-east-1aws ec2 delete-subnet --subnet-id subnet-0729e993842e07ad7 --region us-east-1aws ec2 delete-security-group --group-id sg-0770cff403a4005c7 --region us-east-1This way clean-up process would be complete.
Lab files
- None